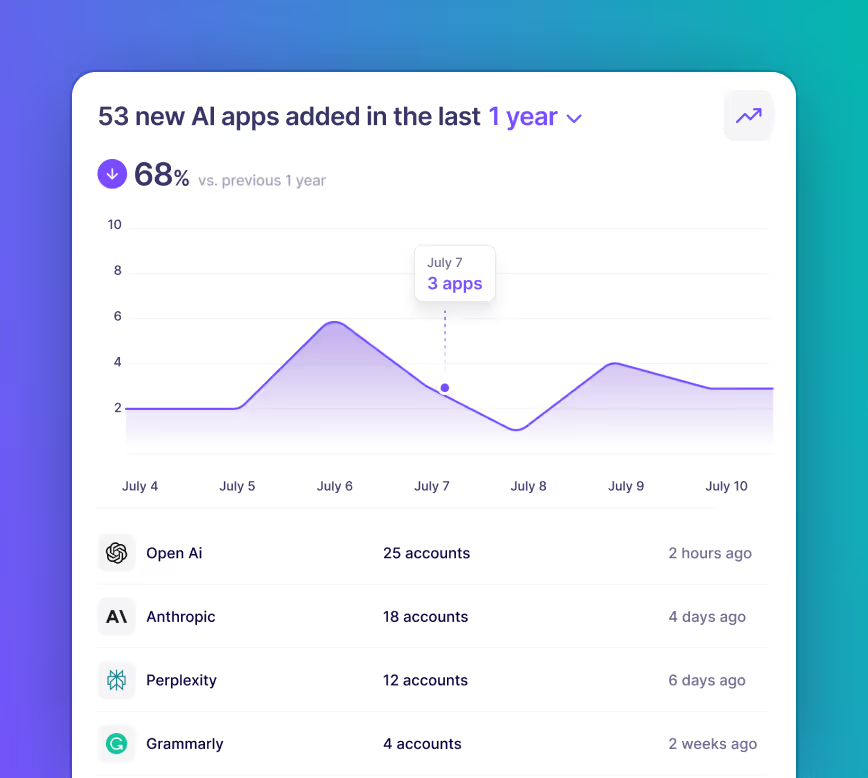
Find shadow AI including apps, agents, and integrations, even apps introduced without IT approval.



Modern security teams ❤️ Nudge Security


Common questions about Nudge Security's shadow AI solution

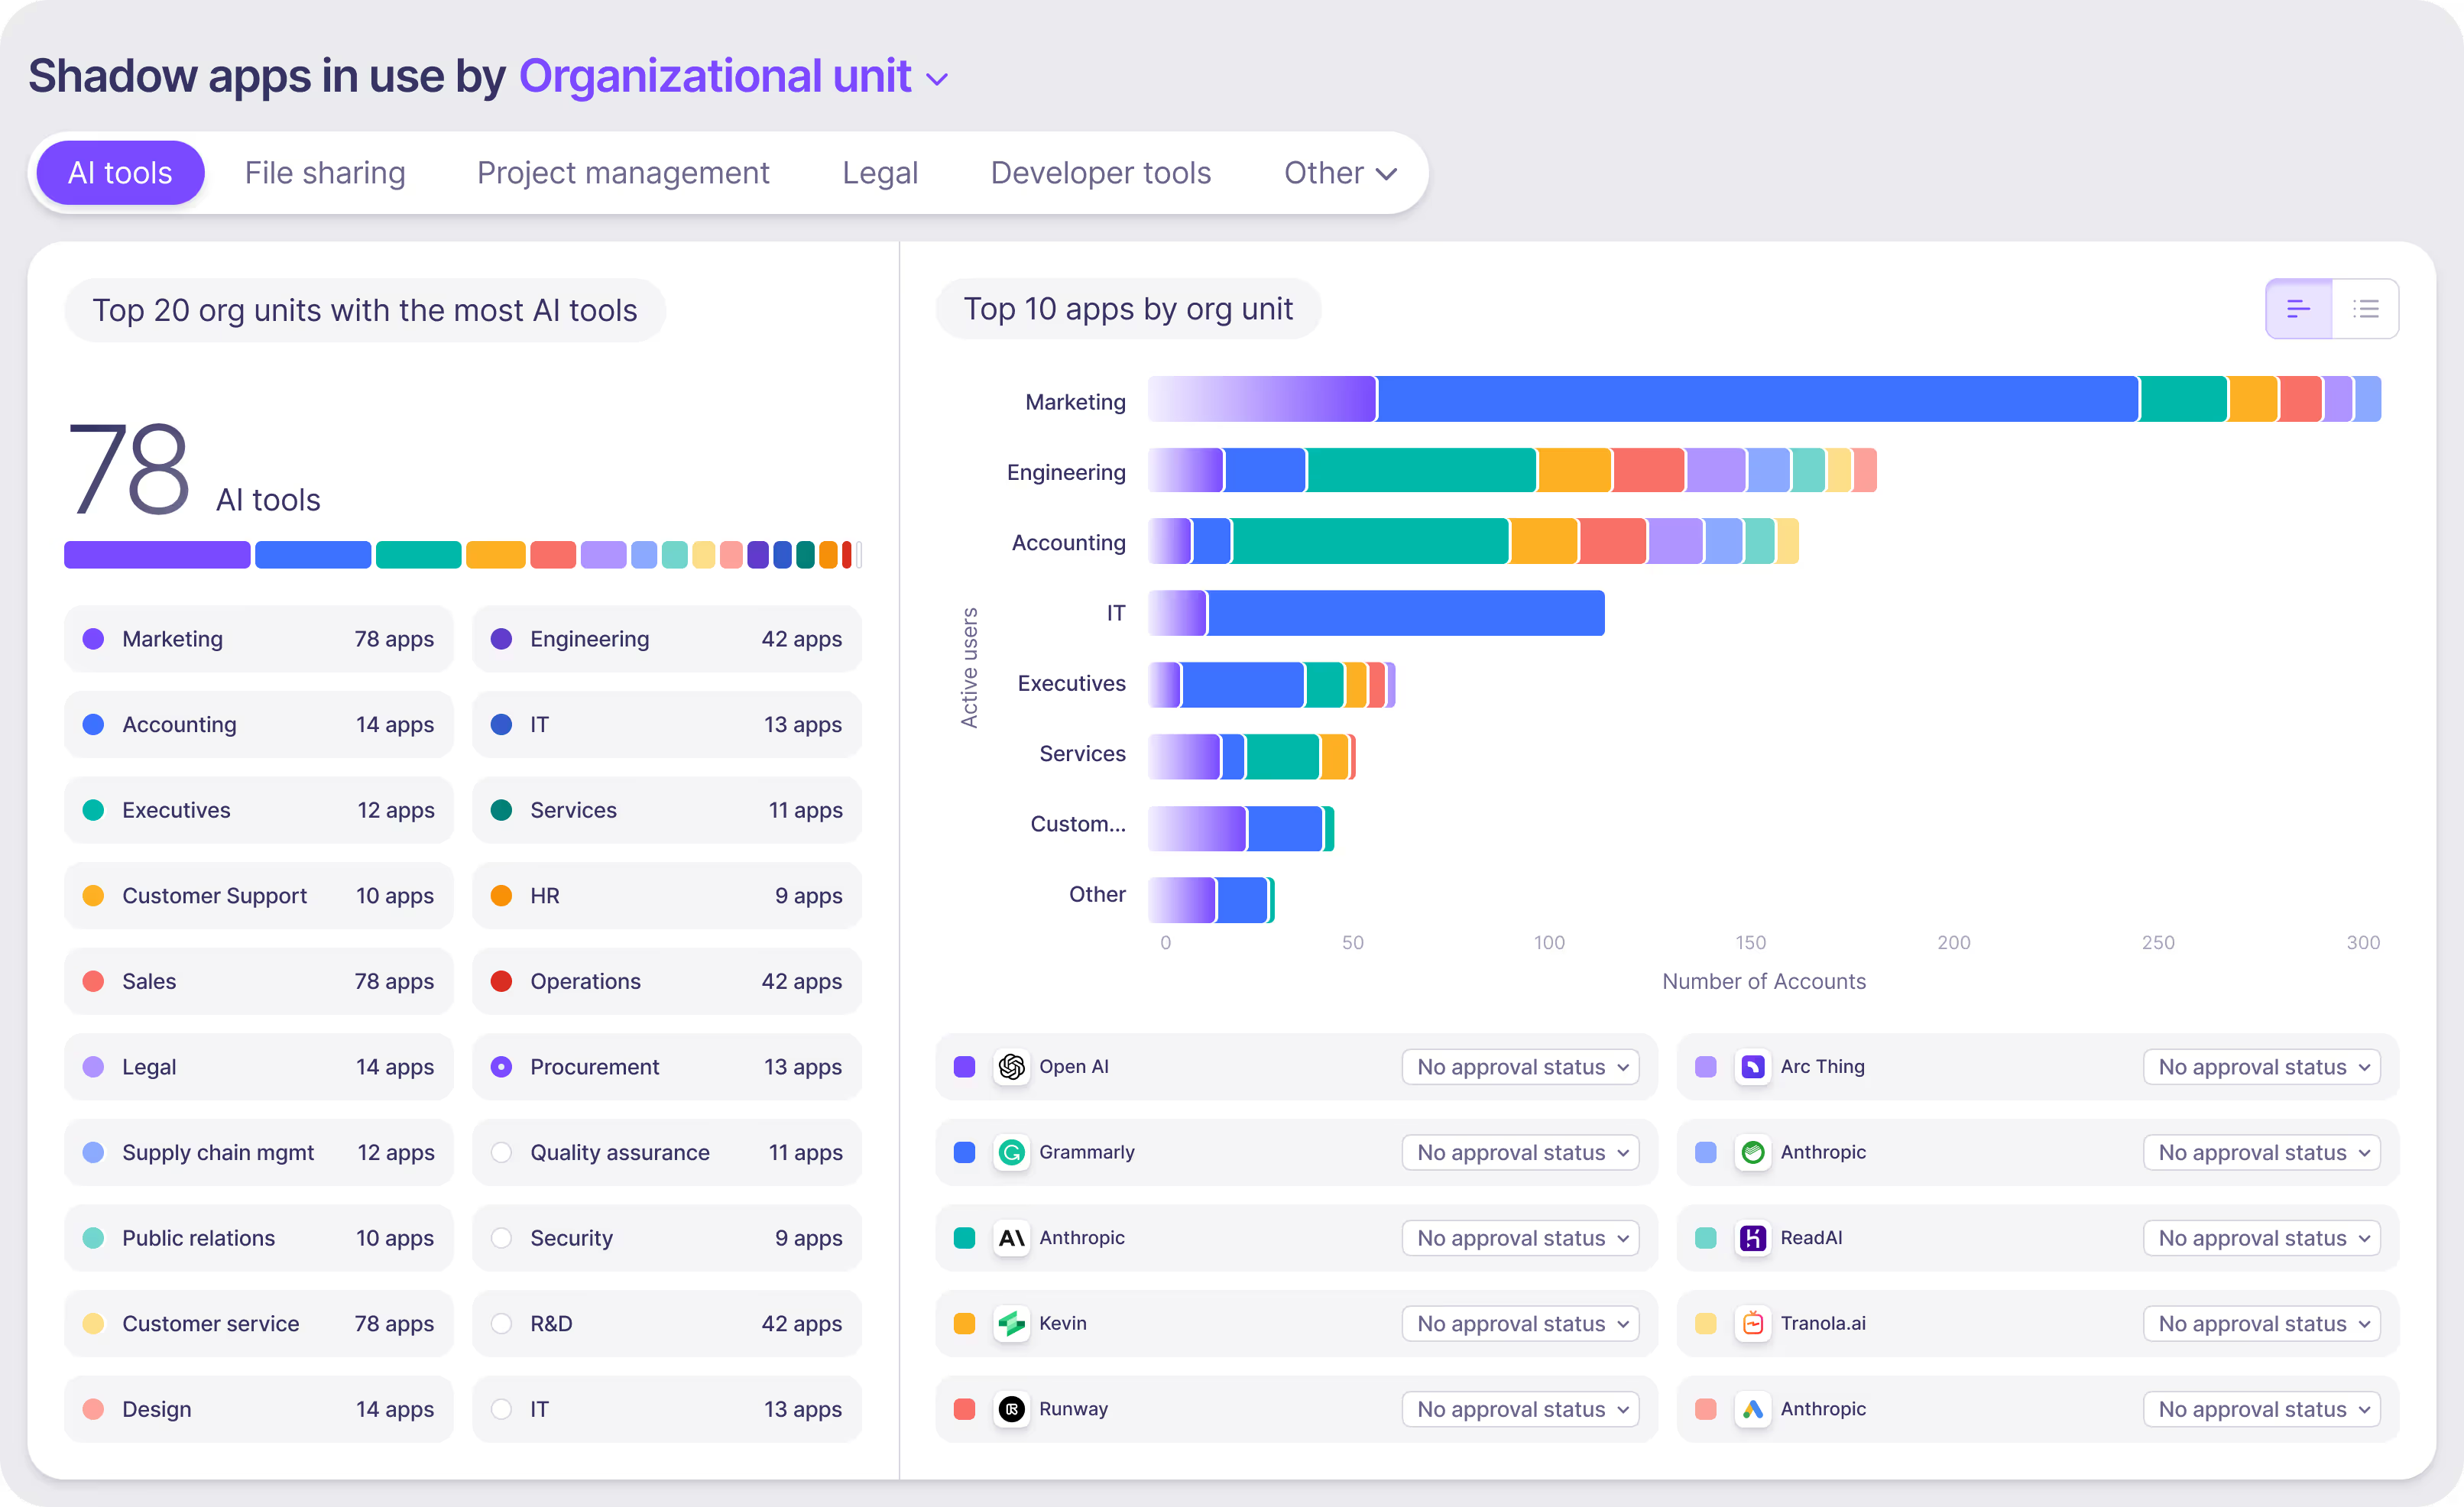
Fast. Most organizations have a complete AI and SaaS inventory in under two hours. Nudge Security automatically discovers and classifies AI apps, even those you’ve never heard of before and those introduced in the past. From there, Nudge Security continuously updates your inventory as new apps and accounts are introduced, so you always have an accurate system of record for AI use. And, you can configure alerts and workflows to trigger immediate notifications and actions when new apps or accounts are introduced.
Nudge Security uses a layered approach to discover AI use, starting with email-based discovery that works via a lightweight integration into your organization’s email provider (Microsoft 365 or Google Workspace) and analyzes emails received from SaaS and AI providers to identify account creation and other activity related to AI tools. From there, you can deploy our browser extension to gain deeper, real-time insights into frequency of AI use, file upload activity, password hygiene, and more. Nudge Security also offers API integrations into your business critical SaaS apps so you can monitor for integrations with AI tools that could allow data access.
Nudge Security can detect virtually any AI tool being used in your organization, including popular options like ChatGPT, Claude, DeepSeek, Perplexity, Gemini, and those you've never heard of. Our platform uses machine learning to recognize new AI tools as they emerge, without the need for new discovery rules to be added, or the need for you to input a list of tools to look for. This approach ensures you maintain visibility even as the AI landscape evolves.
Yes. Nudge Security uses two complementary discovery channels to find the agents employees build across enterprise platforms. API-based discovery covers platforms that expose AI agent details via an API (like Salesforce Agentforce, Microsoft Copilot Studio, Google Gemini, ServiceNow, n8n, Tines, ChatGPT, Abacus.AI, and Workato). Browser-based discovery covers platforms without APIs—like Cursor, OpenAI Agents Workflows, ChatGPT workspace agents, Atlassian Rovo, Retool, and more—using the Nudge Security browser extension.
For every agent discovered, you see who built it, what it connects to, what permissions it holds, and what risks it carries. From there, you can set approval status, assign a technical contact, and nudge the creator to confirm intent and remediate risk.
Yes. Nudge Security discovers MCP server integrations via our analysis of OAuth grants enabled by connecting to your IdP. Nudge can also discover MCP integrations via our connected apps, API integrations that can be enabled with your business critical SaaS apps to monitor for risky integrations, security misconfigurations, and identity security risks.
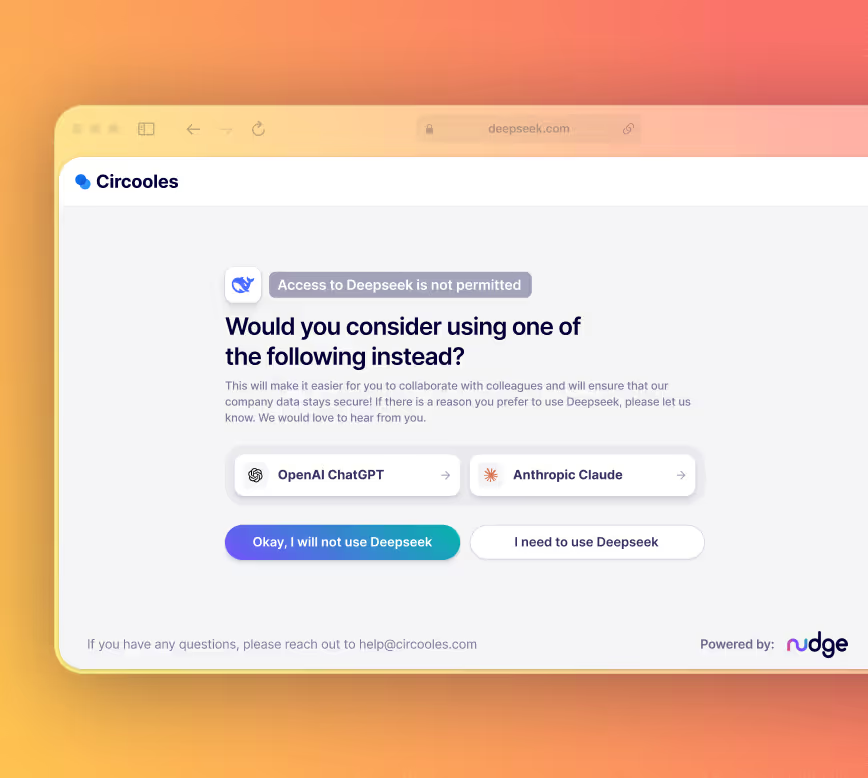
Nudge Security's AI conversation monitoring works through our browser extension, which provides real-time visibility into how employees interact with AI tools. The extension monitors for key activities such as file uploads, copy-paste events, and API key usage, giving you the ability to stop sensitive data from being shared with AI chatbots. Monitoring happens directly in the browser without requiring network proxies or endpoint agents, allowing you to detect risky behaviors and redirect users to secure options as they are working.
Nudge Security discovers and inventories the SaaS-to-AI integrations enabled via MCP, API, webhooks, and other app marketplace connectors that share potentially sensitive enterprise SaaS data with third-party AI tools and agents. Additionally, you can use our growing list of connected apps to gain deeper visibility, including API integrations with AI apps. This gives you comprehensive visibility into where AI tools have been granted access to other systems, by whom, and what level of access was granted.
Only Nudge Security uncovers shadow AI and automates guardrails for safe AI adoption as part of a complete workforce security solution.
Refer to these resources for more detail on how we compare to other solutions for securing AI use:
Nudge Security is built with privacy and security at its core. It typically requires read-only access to accounts, analyzes data in memory, and only stores metadata necessary for reporting and governance. Sensitive content, such as emails or documents, is not retained, and every action is auditable. This ensures organizations can gain visibility into shadow IT while maintaining compliance with internal privacy policies and external regulations. To learn more about how we limit and safeguard our access to your email account, visit our Trust & Security page.
Additionally, Nudge Security is SOC 2 compliant. Visit the Nudge Security Trust Center for our SOC 2 Type 2 report and other compliance documentation, or reach out directly at [email protected] with any questions.