Only Nudge Security can map your entire SaaS and AI supply chain—today.


Only Nudge Security can map your entire SaaS and AI supply chain—today.
Only Nudge Security can map your entire SaaS and AI supply chain—today.






Breaches like the Salesloft-Drift OAuth token compromise show attackers don't need to breach you directly—they just need one vendor with access to your data. Those blind spots multiply every time an employee connects a new app or grants an integration.


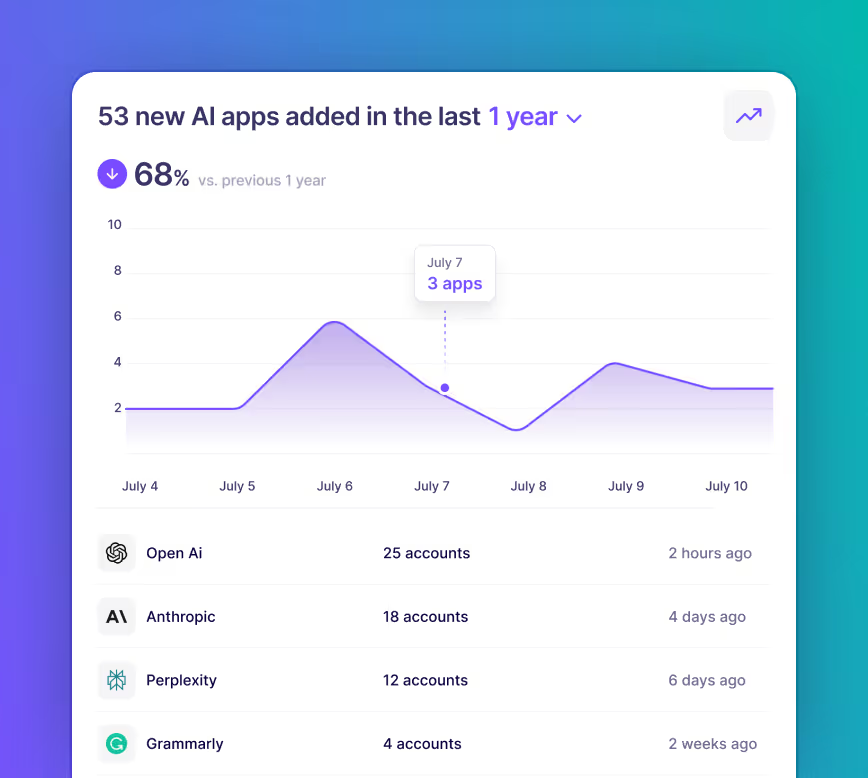
Inventory and triage your SaaS and AI on Day One with patented, perimeterless SaaS and AI discovery across multiple vantage points.


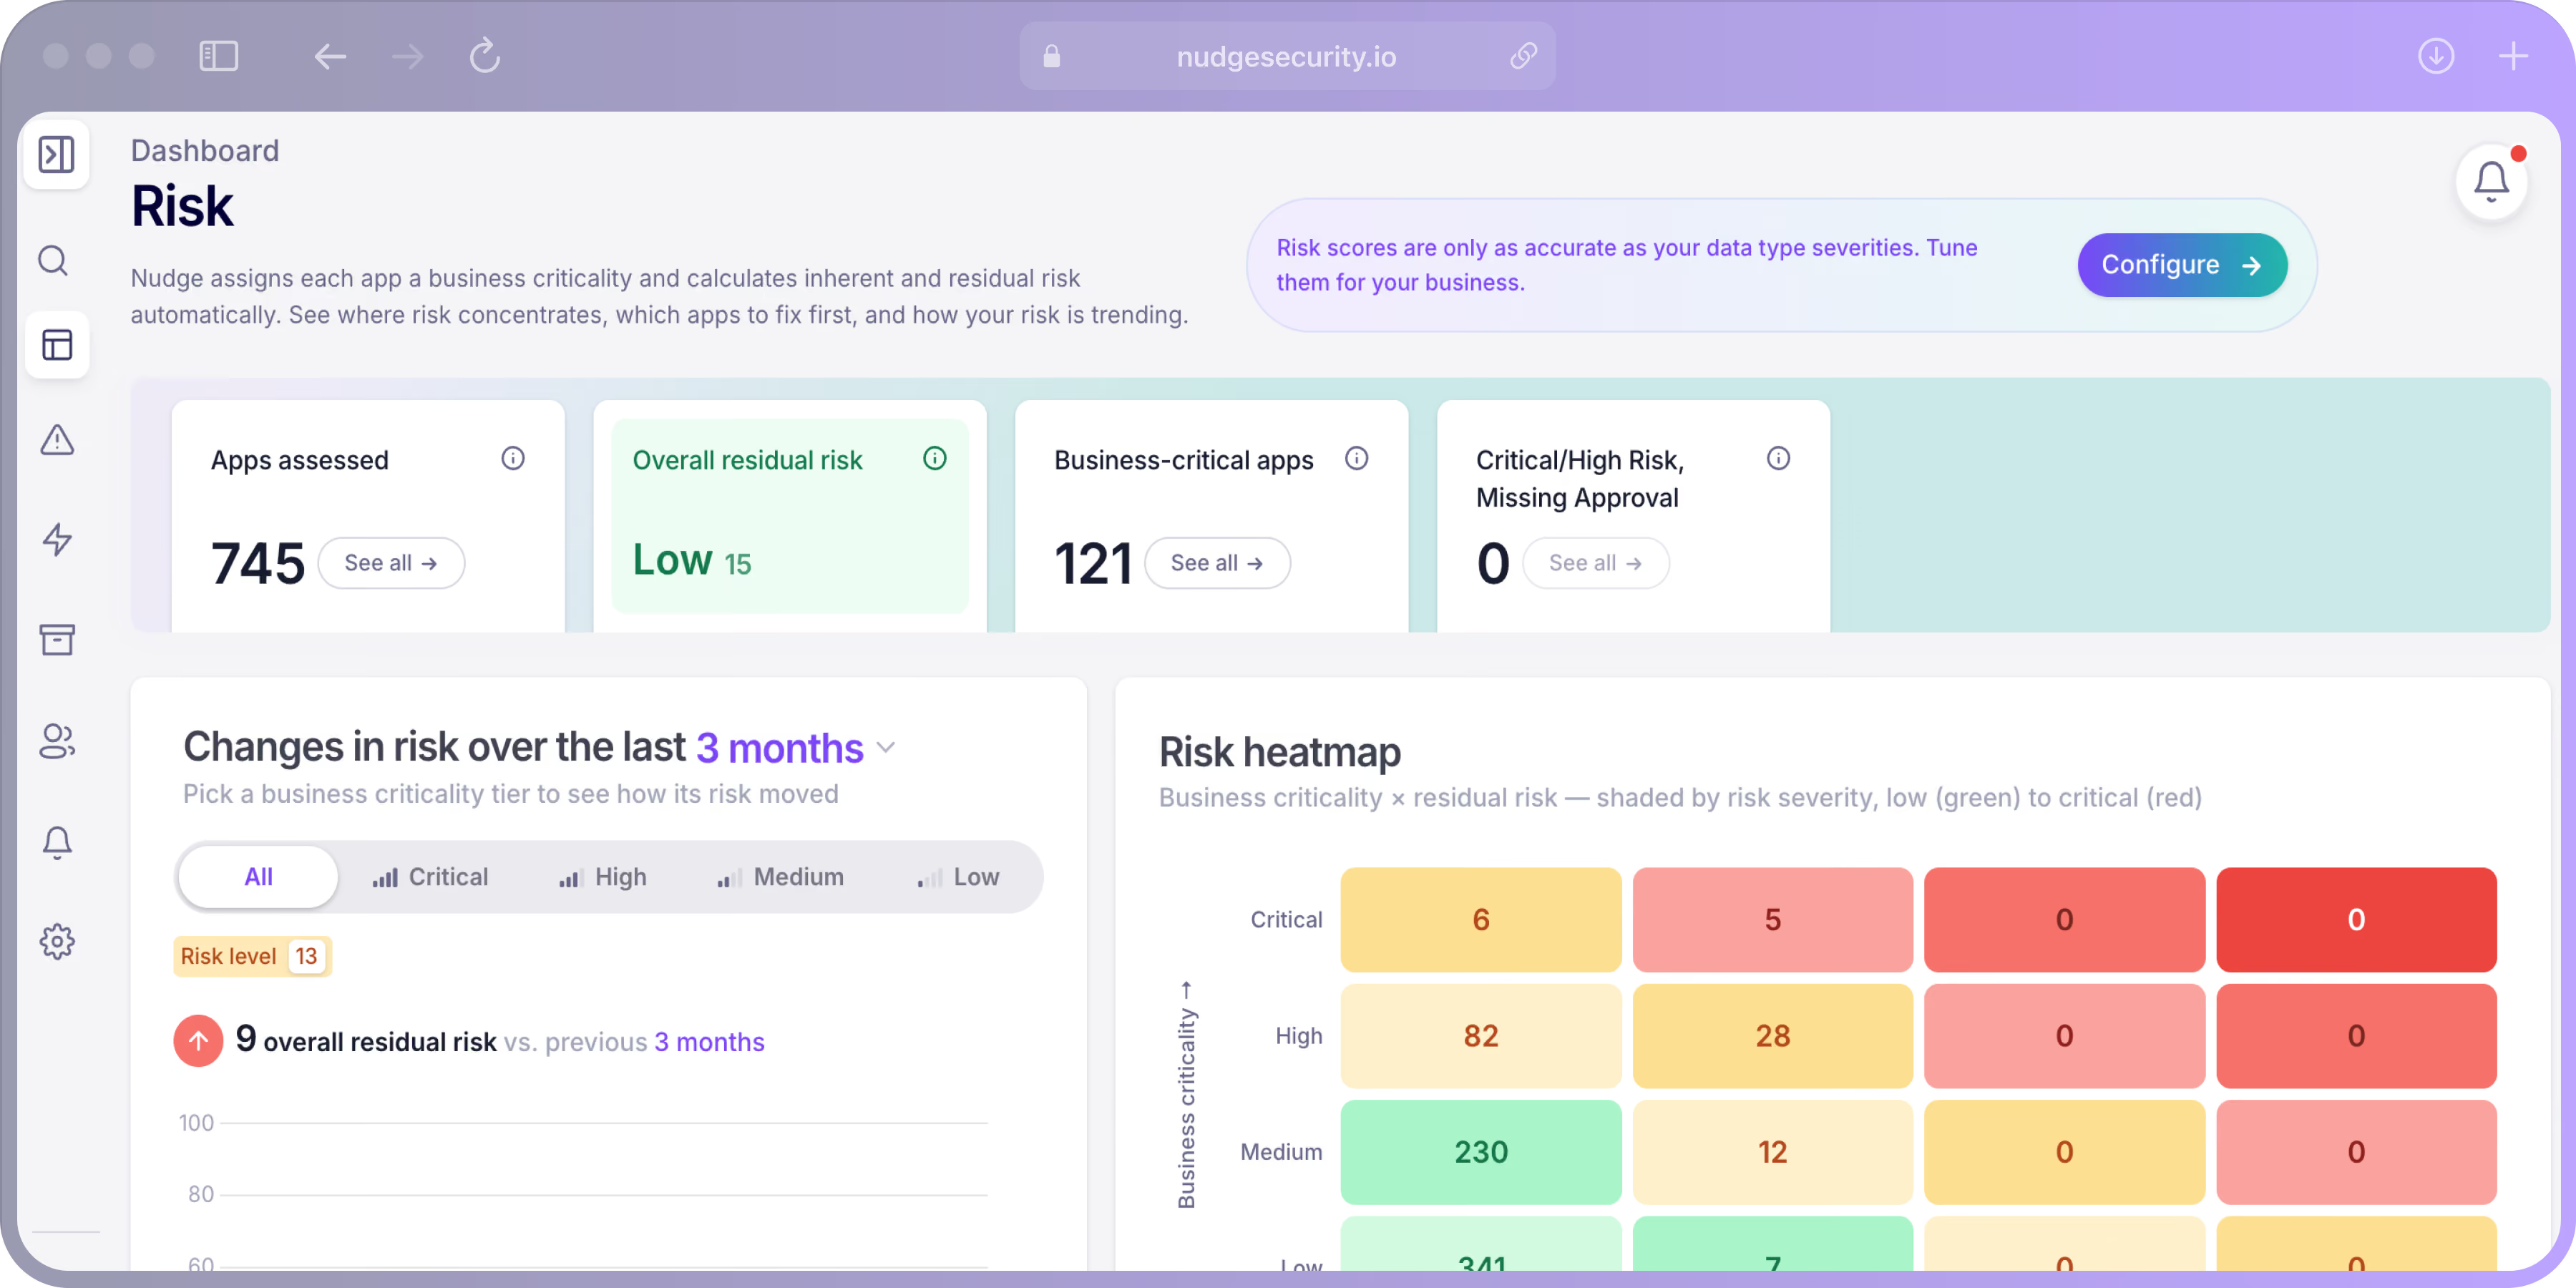
Accelerate vendor security reviews with always-on risk scores and a detailed breakdown of risk factors, drawn from rich internal usage context and proprietary intelligence for 250k+ vendors.
Stay on top of evolving risk—without manual reviews.

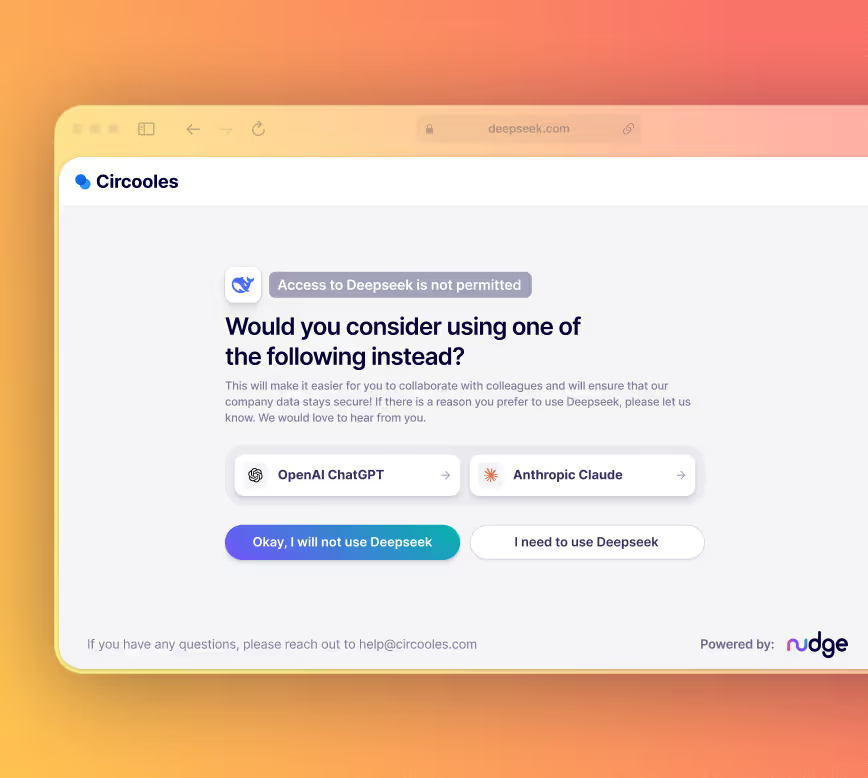
Agentic AI and automated remediation workflows continually reduce risk at scale with security oversight and auditable reporting.

Risk is assessed during vendor procurement and treated as static, even as vendor posture, app usage, and access change.
Security teams lack visibility into shadow SaaS and AI, leaving many apps, integrations, and non-human identities outside risk-management processes.
Generic vendor scores are disconnected from internal context such as data sensitivity, authentication, OAuth grants, configurations, and compensating controls.
Teams manually investigate changing risks and struggle to determine which apps and control gaps require attention first.
Mitigating controls lag behind evolving risks, allowing new integrations, broader access, and changing app criticality to create unaddressed exposure.
SaaS and AI apps are continuously discovered and auto-tiered by criticality based on the scope of organizational adoption and the sensitivity of inferred data types.
Dynamic app risk scores combine vendor, supply-chain, and breach intelligence with each app’s internal usage, access, identity, integration, and control context.
Specific control gaps are continuously surfaced and ranked by their potential impact, showing security teams what to fix first.
Findings, remediation workflows, and recommended controls adapt as an app’s risk posture changes.
Policy-driven nudges and guided workflows engage the right app owner, administrator, or user to reduce risk at scale while preserving human oversight.
Common questions about Nudge Security's third-party risk management solution

Yes. Nudge Security maps connections beyond your direct vendors, surfacing fourth-party exposure: apps your vendors are connected to that could introduce risk into your environment through the supply chain.
Yes. OAuth connections are a core part of Nudge Security's TPRM coverage. Each connection is risk-scored based on permission scope and data access, and you can revoke high-risk connections with a single click.
SaaS third-party risk management is the practice of identifying every vendor connected to your organization's SaaS environment, assessing their security posture, and monitoring for supply chain breaches in real time. In a SaaS-first org, third-party risk grows every time an employee connects a new app or grants an OAuth integration.
Nudge Security monitors your third- and fourth-party supply chain in real time, alerting your team when a connected vendor is breached and identifying which users in your organization had active accounts or integrations with the affected vendor.
In SaaS-first organizations, vendor relationships multiply at the speed of employee adoption: every OAuth grant, API connection, and app marketplace integration adds a new third party to your risk surface. Most TPRM programs were built for a world where vendor relationships went through procurement. They weren't designed to track this volume of connections continuously.
Nudge Security discovers every SaaS and AI vendor introduced across your organization, including vendors employees connected directly without IT involvement, and inventories their app-to-app integrations and OAuth connections alongside them.
Nudge Security draws on a database of over 200,000 vendor security profiles, providing security details, breach histories, and compliance attestations for each vendor discovered. This lets your team prioritize review and remediation based on actual risk rather than vendor prominence.