Tackle sprawling OAuth grant risk at scale with the OAuth Grant Risk Analyst.
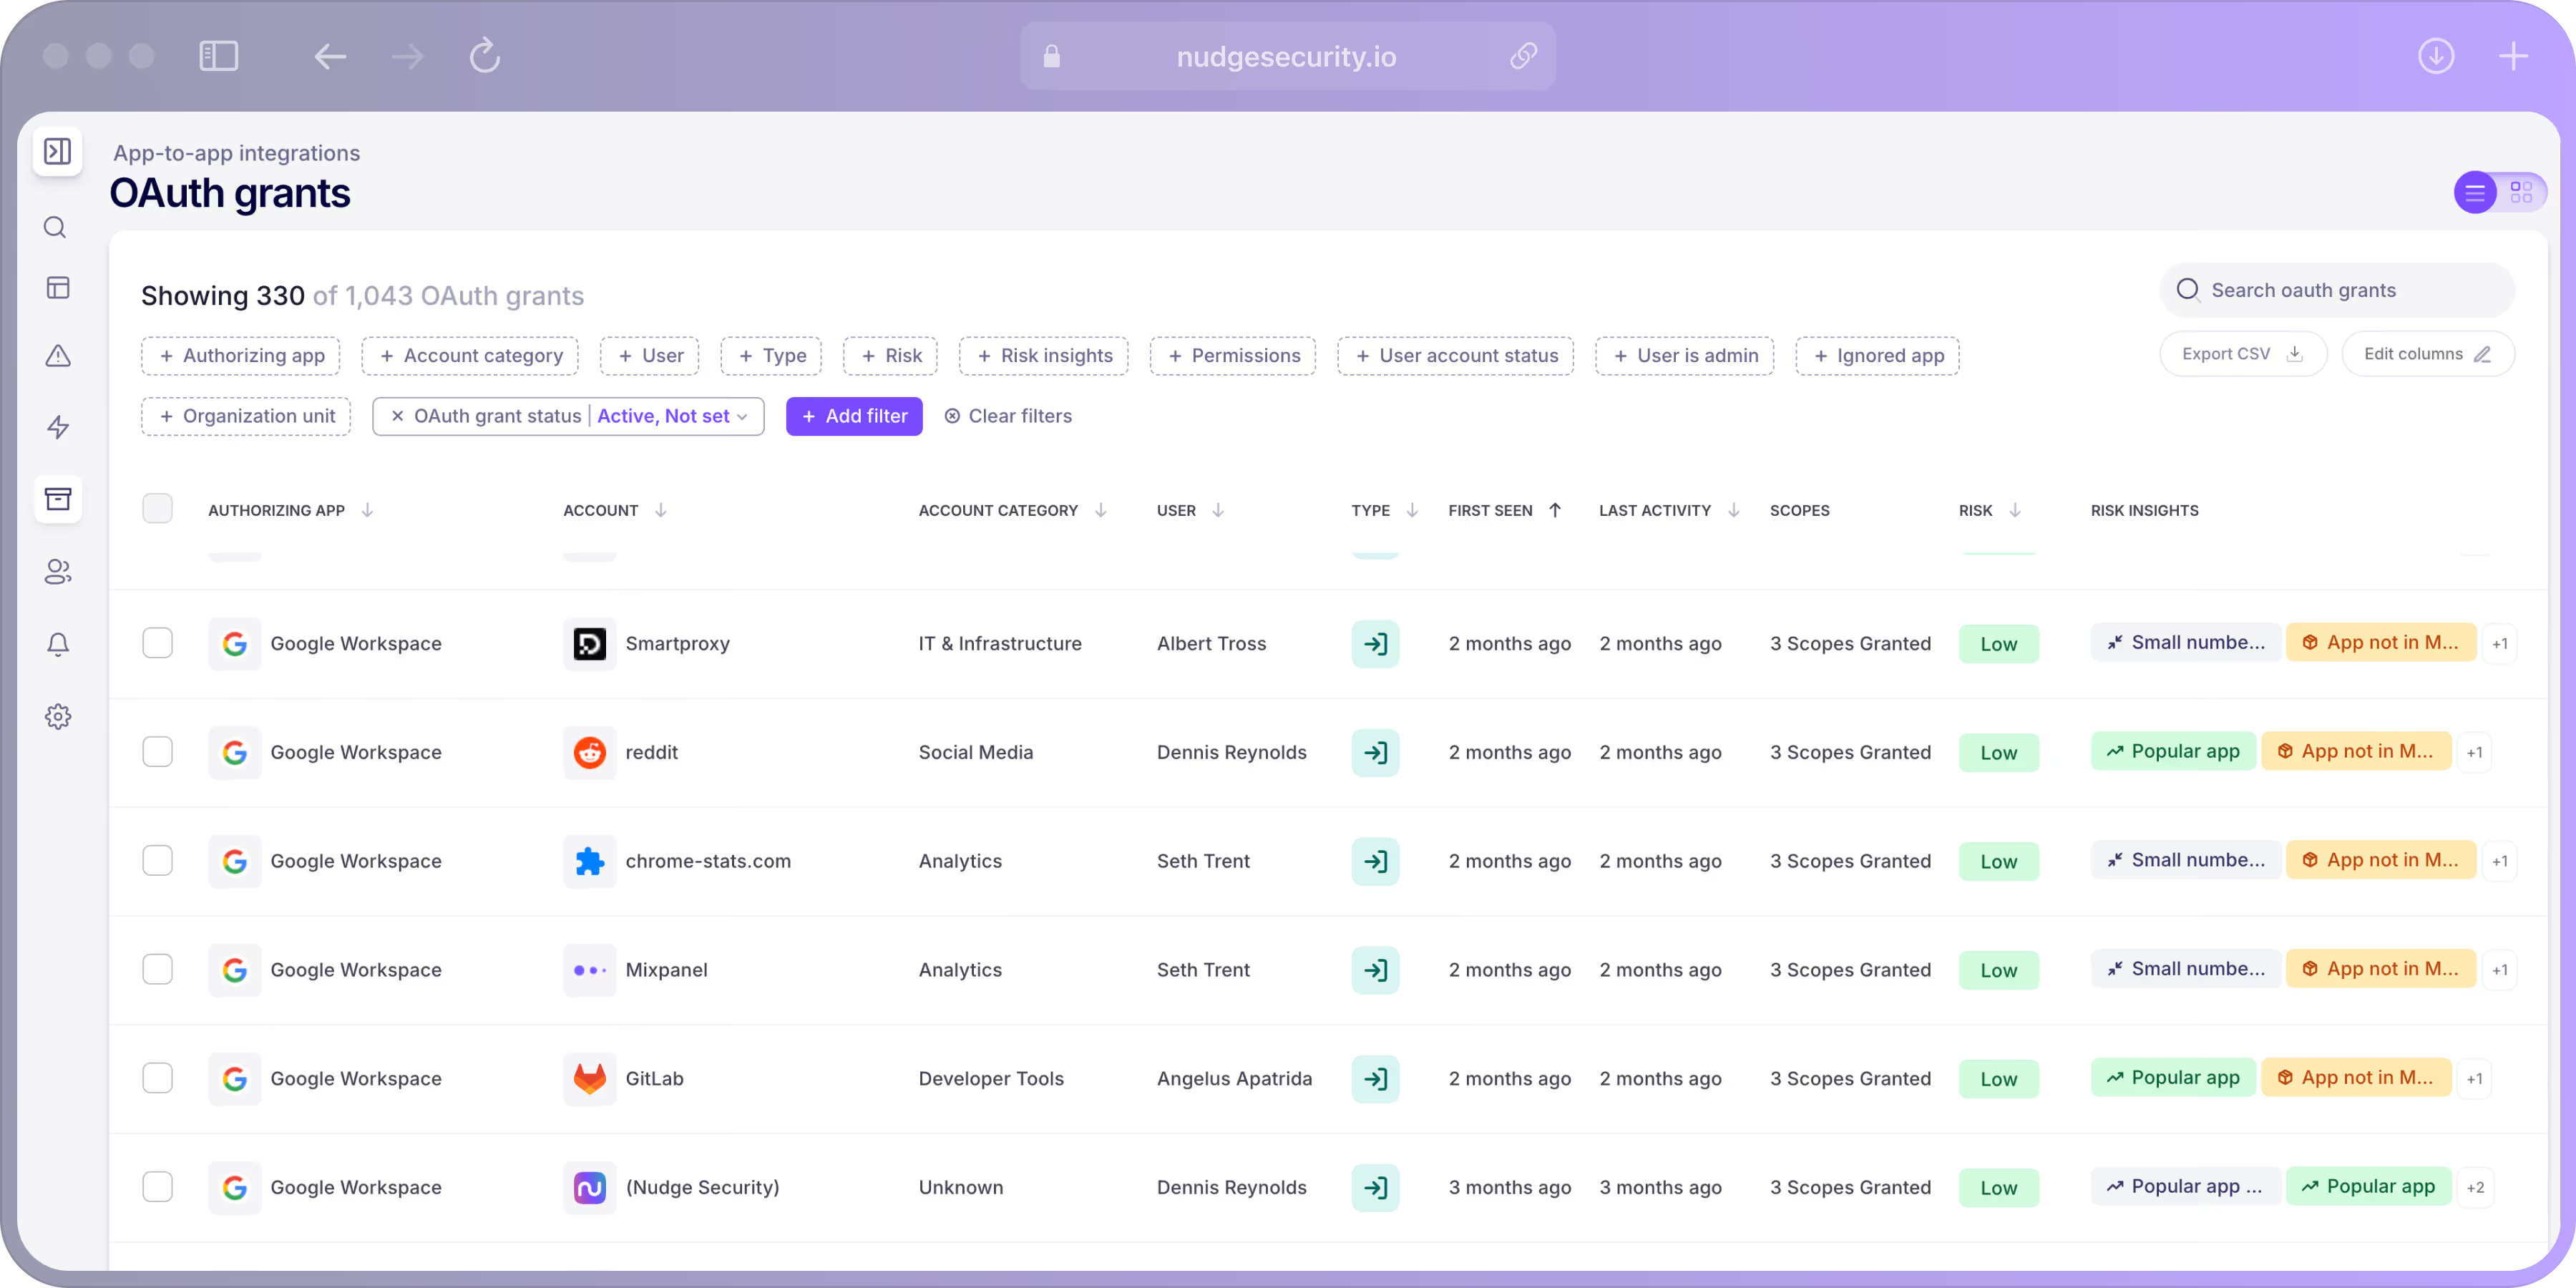


Tackle sprawling OAuth grant risk at scale with the OAuth Grant Risk Analyst.
Tackle sprawling OAuth grant risk at scale with the OAuth Grant Risk Analyst.


Breaches like Salesloft-Drift prove attackers don’t need to target your core systems directly. They can exploit the hidden web of SaaS apps, OAuth grants, and third-party dependencies—blind spots your traditional security tools will never see.


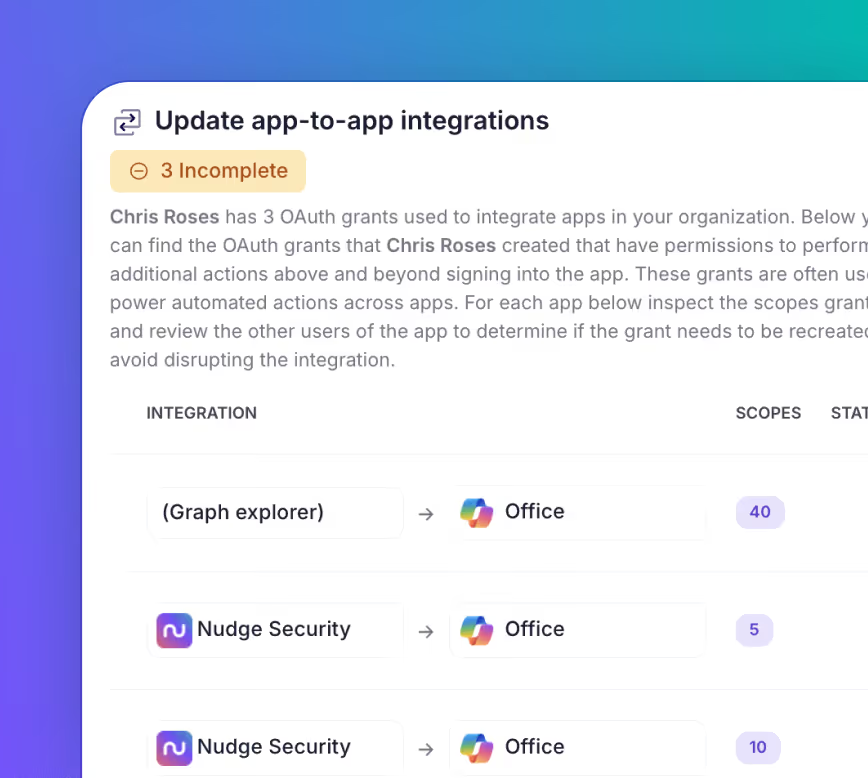
Nudge Security provides a complete inventory of OAuth grants and app-to-app integrations across your SaaS estate, including remote MCP connections.

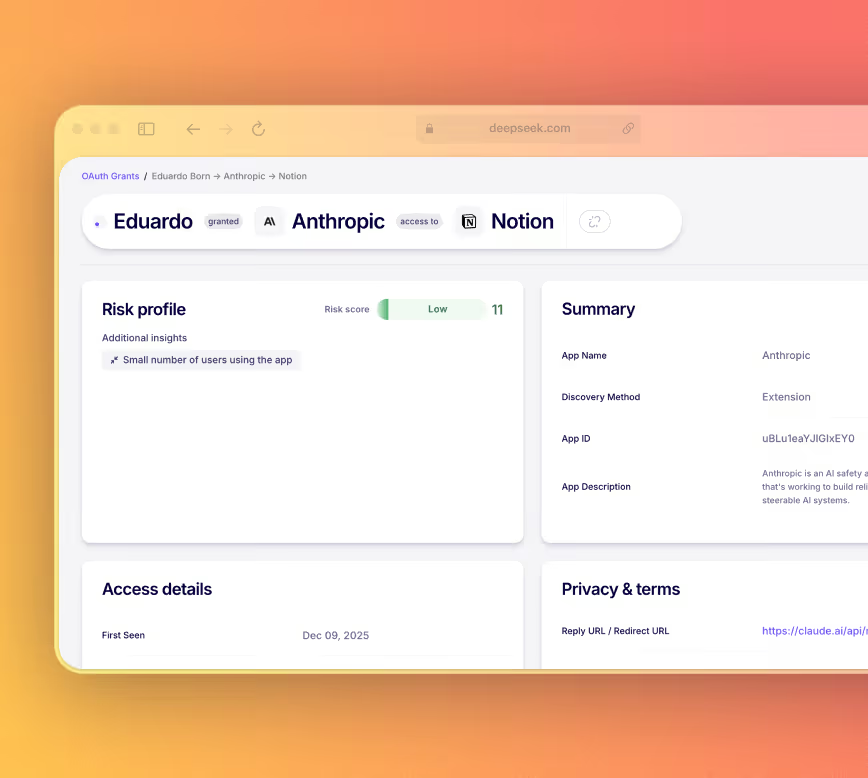
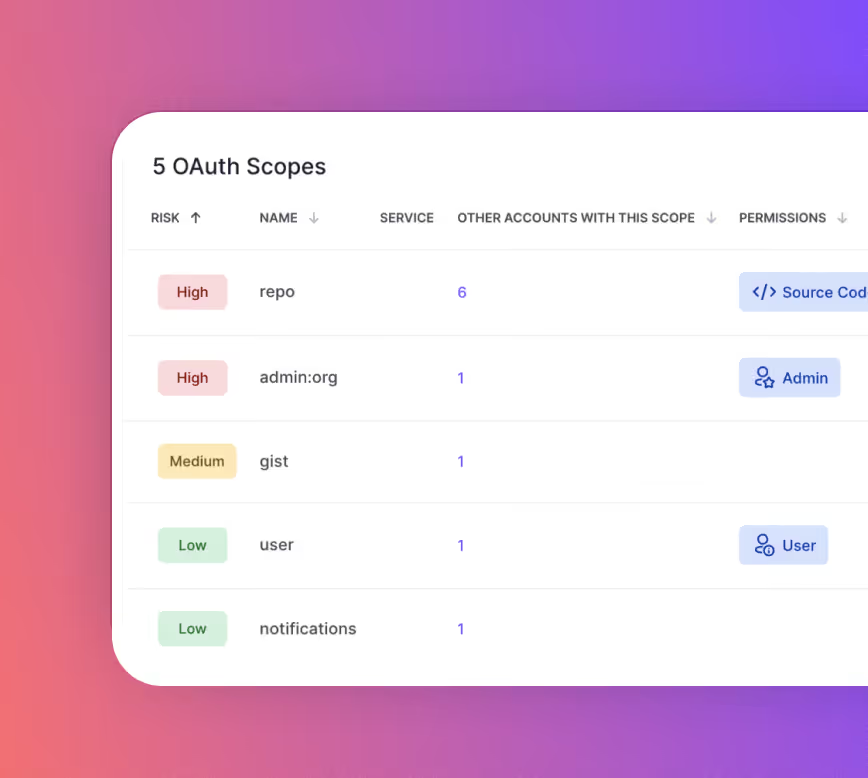
Nudge Security automatically classifies and risk-scores every integration based on the scope of permissions, the vendor, grantor, org usage, and the sensitivity of the data being accessed.
Nudge Security makes it easy to review and revoke sprawling app-to-app integrations, helping you to maintain a strong security posture.

Blind spots: unsanctioned apps, shadow vendors, unknown OAuth permissions
Long vendor reviews, sporadic audits, manual detection
Permissions drift, stale or excessive access left unchecked
Compliance & risk posture unclear; slow response to breaches
Full visibility: known & unknown apps, integrations, vendor dependencies
Continuous, automated risk detection, instant alerts, workflow driven
Least-privilege enforced, unused permissions revoked, identity drift controlled
Auditable, proactive posture management; breach detection; rapid remediation
Common questions about Nudge Security's OAuth risk management solution

Nudge Security discovers remote MCP server connections through OAuth grant analysis, identity provider integrations, and API connections to business-critical SaaS apps.
Nudge Security's research found an average of 70 OAuth grants per employee, with roughly 40 apps per organization carrying programmatic access to sensitive corporate data. For a 500-person company, that's tens of thousands of third-party connections to govern.
OAuth risk management is the practice of discovering, assessing, and governing every third-party app connection that has been granted access to your organization's core SaaS platforms. Most organizations have dozens of these connections per employee, many of which are overprivileged, unused, or from vendors with poor security posture.
Yes. Nudge Security lets you revoke unused or high-risk OAuth grants directly, send verification requests to the employees who authorized them, and automate revocation as part of your SaaS employee offboarding workflow.
OAuth grants give third-party apps direct access to your data, and most employees grant them without reading the permission scope. Those grants persist indefinitely unless explicitly revoked, and they survive password resets and even a complete employee offboarding process. A single compromised third-party app can become an access path into your environment.
Nudge Security automatically inventories every OAuth grant across your SaaS estate and maps the permission scope each one carries. It also surfaces API keys, service accounts, and remote MCP server connections alongside OAuth grants, giving you a complete picture of all programmatic access.
Each OAuth connection is scored based on permission scope and data sensitivity. Nudge Security flags connections with access to high-value data, including email, files, and code repositories, and surfaces patterns it calls "data highways": connections with unusually broad, persistent access.